Newsletter Subscribe
Enter your email address below and subscribe to our newsletter
[forminator_form id="25163"]

All voices matter
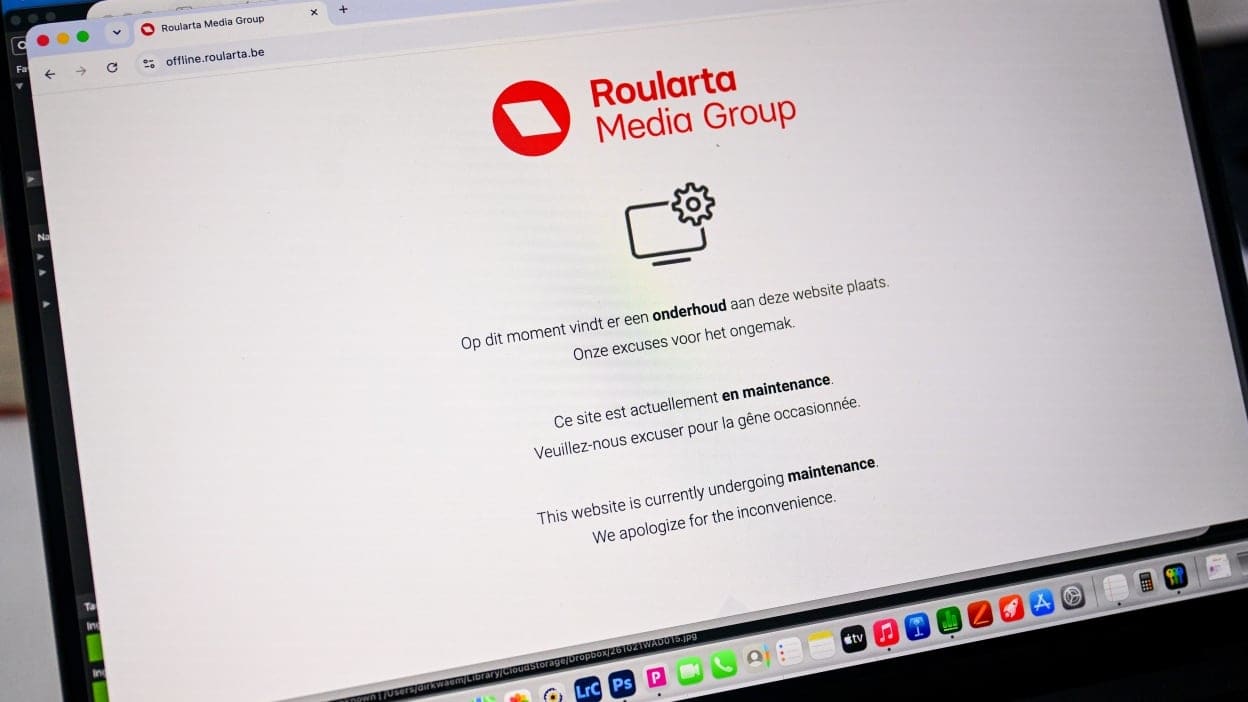
reuters.com+1.cloud.google.com+1.reuters.com+2.Government websites across Europe and Canada went offline on Wednesday, October 21, after PHP developers released emergency fixes for two critical flaws in the programming language. PHP runs a large share of the public web. "All servers using any version of PHP released in the last 20 years will be vulnerable," Drupal Association interim chief executive Tiffany Farriss told Reuters.openai.com
The bugs are tracked as CVE-2026-109618 and CVE-2026-109619. Each carries a critical severity score of 9.2 and can let attackers run code remotely without logging in, according to Google Cloud. The fixes shipped in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35. PHP 8.1 and older versions are past end of life and will not get patches, per CERT-EU. "All PHP users are strongly encouraged to update immediately," the developers said, as quoted by Cybersecurity Dive.reuters.com+2
The NSA warned that sites that cannot be patched right away should come off the web until they can be, TechCrunch reported. The EU cybersecurity agency ENISA said in a joint statement that organizations should consider cutting exposed applications off from public networks if they cannot fix them immediately.techcrunch.com+1
The Dutch National Cyber Security Centre took its own site down. The Port of Rotterdam, the government portal Overheid.nl and several hospital sites followed. Finland pulled government public network services offline, and France's Interior Ministry put all of its websites into preventive maintenance, according to Reuters. In Canada, Artificial Intelligence Minister Evan Solomon said some federal sites were down as a "precautionary measure." The provincial sites for Newfoundland and Labrador and Prince Edward Island were also offline, CBC News reported.cbc.ca+1
Many servers will be hard to fix. Censys data shows about 1.5 million of 2.6 million hosts run a PHP version with no available fix, Reuters reported. Threat researchers at watchTowr and Sophos have already seen attempts to exploit the bugs. "Whilst nobody has been successful to date, we don't expect that will last long," said Jake Knott, watchTowr's head of threat intelligence, as quoted by Cybersecurity Dive.reuters.com+1
OpenAI said the security firm Calif found one of the flaws using GPT-5.6 Sol through OpenAI's Patch the Planet initiative. Wiz, which is owned by Alphabet, found and reported both flaws on its own. OpenAI called the bugs "one of the most impactful security issues in recent memory." Wiz said it used its Wiz Atlas tool along with Google's Gemini 4 Argon and GPT-5.6 Sol, and that the flawed code had sat in PHP for more than a decade, Reuters reported.openai.com+1
The same technology that found the bugs also makes them easier to exploit. "With AI this is no longer a barrier," Wiz wrote, according to TechCrunch. Security researcher Nicholas Weaver put it this way to Cybersecurity Dive: "We are in the world where you have to apply updates effectively instantly."cybersecuritydive.com+1