



Newsletter Subscribe
Enter your email address below and subscribe to our newsletter
[forminator_form id="25163"]

All voices matter
thehackernews+1imperva+1thehackernews+1Eine kritische Sicherheitslücke zur Remote-Code-Ausführung in Alibabas Bibliothek Fastjson wird aktiv ausgenutzt. Für den betroffenen 1.x-Zweig steht kein Patch zur Verfügung, und Angreifer greifen bereits Produktionssysteme in den USA an.
Die unter CVE-2026-16723 geführte Schwachstelle weist einen CVSS-Wert von 9,0 auf und betrifft die Fastjson-Versionen 1.2.68 bis 1.2.83, also den gesamten Endbereich der mittlerweile archivierten 1.x-Reihe. Alibaba veröffentlichte seinen Sicherheitshinweis am 21. Juli 2026 nach einer verantwortungsvollen Offenlegung durch Kirill Firsov von FearsOff Cybersecurity.imperva+1
Was die Schwachstelle besonders gefährlich macht, ist die niedrige Hürde für eine Ausnutzung. Sie erfordert keine Authentifizierung, keine Benutzerinteraktion, keine AutoType-Aktivierung und keine Gadget-Klasse von Drittanbietern im Klassenpfad. Ein Angreifer sendet präpariertes JSON mit einem schädlichen `@type`-Wert an einen über das Netzwerk erreichbaren Endpunkt, der Eingaben an gängige Parsing-Methoden wie `JSON.parse` oder `JSON.parseObject` übergibt. In Spring Boot Fat-JAR-Bereitstellungen kann die Typauflösungslogik über verschachtelte JAR-URLs missbraucht werden, um vom Angreifer kontrollierten Bytecode zu laden.thehackernews+3
Alibaba hat die Angriffskette auf Spring Boot 2.x, 3.x und 4.x unter JDK 8, 11, 17 und 21 verifiziert.imperva+1
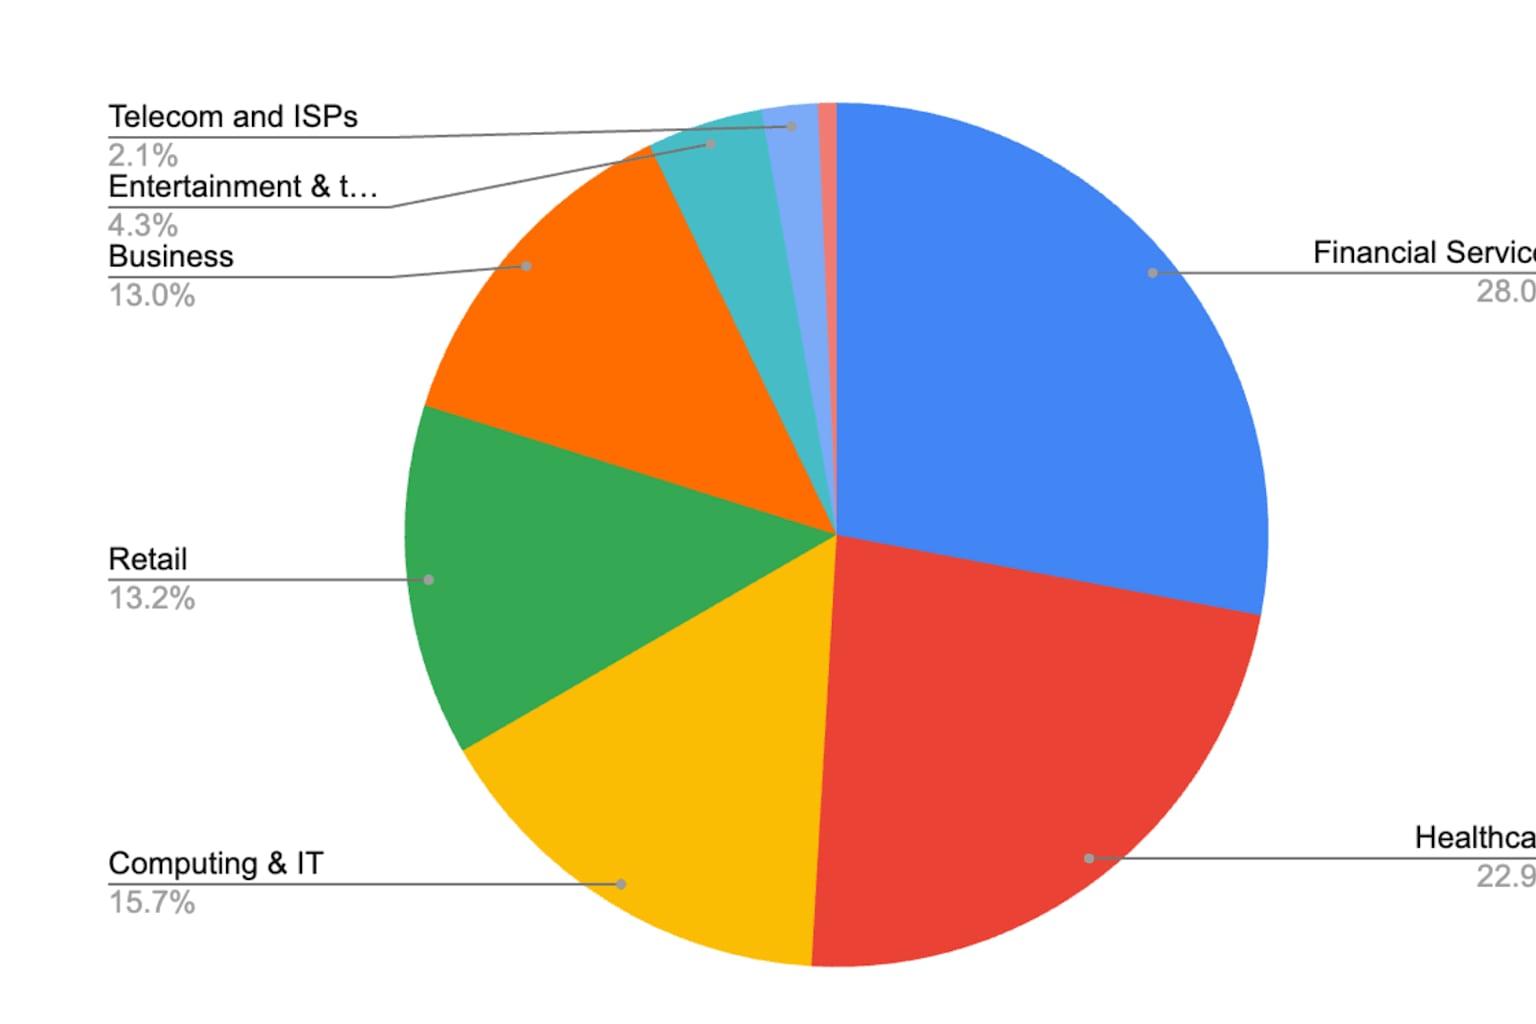
Bis zum 25. Juli hatten sowohl ThreatBook als auch Imperva Angriffe in freier Wildbahn bestätigt. Imperva berichtete von Angriffen auf Finanzdienstleister, das Gesundheitswesen, die IT-Branche und den Einzelhandel, wobei sich die Aktivitäten "fast ausschließlich gegen US-amerikanische Organisationen" richteten, neben einer kleineren Anzahl von Fällen in Singapur und Kanada. Die meisten Angriffe stammten von User-Agents, die Browser nachahmten, obwohl in Ruby und Go geschriebene Tools etwa 30 Prozent des beobachteten Datenverkehrs ausmachten.securityonline+1
Laut SecurityOnline ist mittlerweile ein funktionierender Proof-of-Concept-Exploit öffentlich verfügbar.securityonline
Da Fastjson 1.x nicht mehr gepflegt wird, hat Alibaba keine korrigierte Version veröffentlicht und wird dies voraussichtlich auch nicht tun. Organisationen wird geraten, SafeMode unverzüglich über das JVM-Flag `-Dfastjson.parser.safeMode=true` zu aktivieren, den eingeschränkten Build `1.2.83_noneautotype` zu nutzen oder auf Fastjson 2.x zu migrieren, das den anfälligen Ressourcen-Suchmechanismus nicht verwendet.threatbook+2
Wie The Hacker News anmerkte, war Fastjson 1.2.83 selbst das empfohlene Upgrade für eine separate AutoType-Umfahrung aus dem Jahr 2022. Das bedeutet, dass sich Organisationen, die früheren Empfehlungen gefolgt sind, nun im betroffenen Bereich befinden und keine sichere 1.x-Version zur Verfügung haben.thehackernews


