



Newsletter Subscribe
Enter your email address below and subscribe to our newsletter
[forminator_form id="25163"]

All voices matter
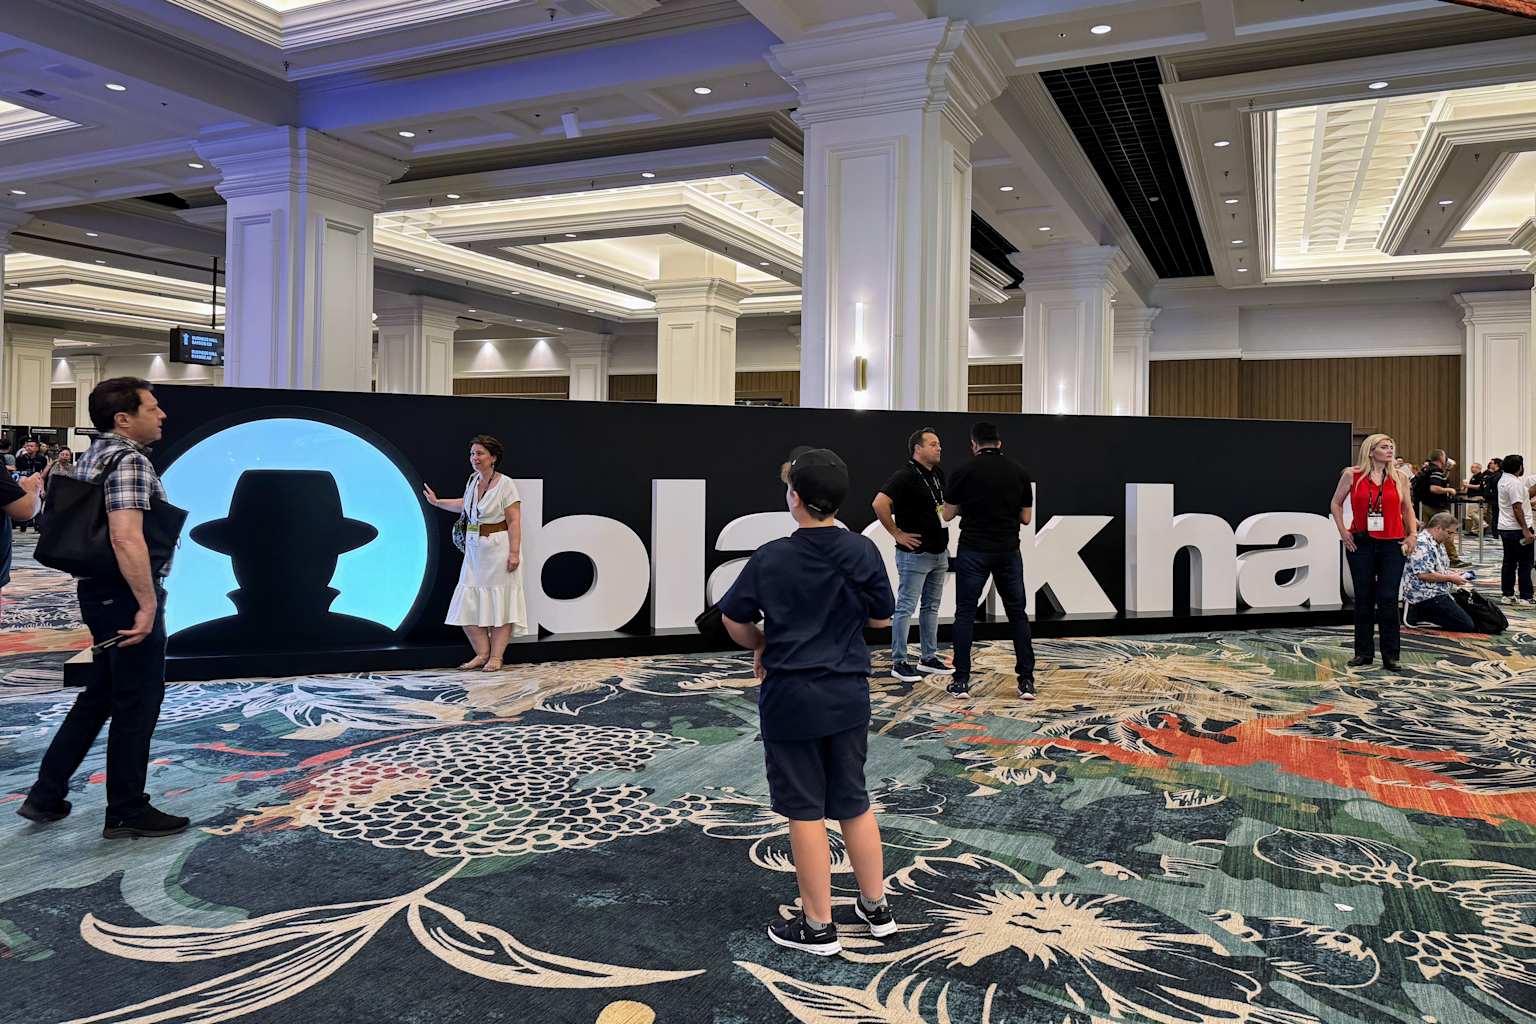
wired+1aiweekly+1wired+1A Greece-based cybersecurity researcher spent nearly two years inside the infrastructure used by North Korean hackers, discovering that 1,640 companies across 57 countries had been compromised by the regime's cyber operations. Vangelis Stykas, CTO at cybersecurity firm Kumio, presented his findings at the Black Hat security conference in Las Vegas this week, offering a rare window into the scale of Pyongyang's hacking apparatus.instagram+1
Stykas told WIRED he accessed multiple command-and-control servers used by the North Korean operators, gaining visibility into approximately 5 terabytes of stolen data, including the hackers' own Slack and Discord communications. In some cases, the attackers had infected themselves with their own malware, inadvertently granting Stykas access to their workstations.instagram+1
Of the 1,640 impacted organizations, Stykas said between 700 and 800 suffered "really damaging" intrusions, including root access to servers, root access to AWS accounts, and cryptocurrency wallet keys. He asked WIRED not to reveal exactly how he initially gained access to the servers due to the sensitivity of the methods involved.wired+2
The attack methodology followed a pattern the cybersecurity industry has tracked in recent years: North Korean operators approach software developers with fabricated high-paying job offers, then send coding tests that secretly install malware and harvest credentials. From there, the hackers escalate to full organizational access.aiweekly
Stykas publicly named roughly a dozen affected organizations at the conference, including Coinbase , Uniswap Labs, Oppo, Boston Children's Hospital, and Italy's Supreme Judicial Council — largely those that responded well to his disclosures or remediated the compromises. Coinbase and Uniswap Labs were among the entities that responded after receiving warnings from Stykas.bitcoinworld+2
The findings add to mounting evidence of North Korea's cyber capabilities targeting the cryptocurrency sector. In April, researchers at Arctic Wolf documented a separate North Korean campaign using fake video calls to target over 100 blockchain and DeFi executives across more than 20 countries.cybersecuritydive
Stykas described the hackers' focus as unmistakable: despite having access to sensitive medical records and criminal databases, the operators prioritized cryptocurrency wallets and blockchain access rights. "It's keys, it's blockchain access, it's ridiculous access," Stykas told WIRED.instagram+1


