Newsletter Subscribe
Enter your email address below and subscribe to our newsletter
[forminator_form id="25163"]

All voices matter
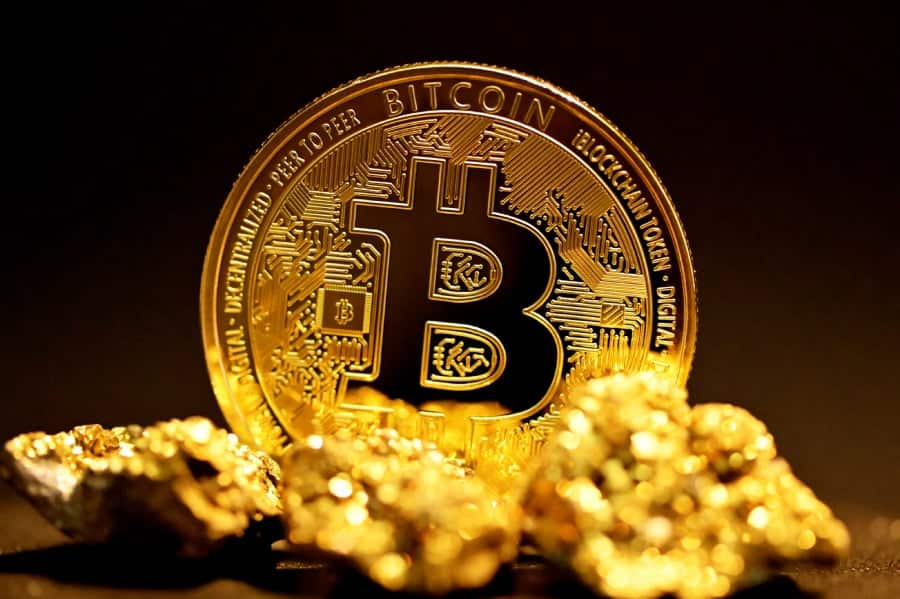
gizmodocryptobriefing+1gizmodoHackers who drained roughly $320 million in Bitcoin from Blockstream's Liquid Network on September 6 have escalated their demands, switching from encrypted messages to public plaintext ultimatums on the Bitcoin blockchain and insisting on a 10% bounty paid from the company's own funds.
The attack exploited a range-proof verification cache bug in the Elements software, the open-source codebase underpinning the Liquid sidechain, according to blockchain security firm Chainalysis. The flaw allowed the attackers to mint unbacked L-BTC tokens that the system treated as valid, then convert them into real bitcoin through SideSwap's peg-out service. Roughly 4,000 BTC — about 95% of the federation wallet's reserves — was withdrawn in a single transaction, Reuters reported.reuters+3
No federation keys were compromised. The Liquid Network operates on an 11-of-15 multisig model, and the multisig itself held up; the failure was in the upstream validation software. SideSwap, whose automated system processed the withdrawal without size or velocity checks, accepted responsibility for how a Liquid-layer fault became a mainchain loss and returned its roughly 4 BTC fee to the federation.cryptobriefing+1
After Blockstream patched the vulnerability and updated its nodes, the attackers returned 3,400 BTC but kept 598.5 BTC, worth about $47 million, as a self-appointed reward. The two sides initially negotiated through PGP-encrypted OP_RETURN messages on the Bitcoin blockchain. But talks appeared to sour — the hackers sent a two-character plaintext note, ":(", before announcing all future messages would be unencrypted.therecord+2
Their public ultimatum accused Blockstream of allocating as little as $1.5 million to secure $5 billion in assets. "You SHALL pay 10% using your own money as bug bounty or you will cause all your holders a 15% loss for your irresponsibility and stinginess," the attackers wrote in a Bitcoin transaction. The 10% figure implies they are willing to send back additional funds, keeping roughly $32 million rather than the current $47 million.gizmodo
The white-hat framing has drawn sharp criticism. Ledger CTO Charles Guillemet called the demand "straight extortion," arguing that responsible disclosure would have involved contacting Blockstream's security team privately so the network could be paused and patched before any funds moved. Bitcoin Core contributor Greg Sanders dismissed the hackers' complaints about Blockstream's spending: "Robbing a fancy bank, trying to keep a double digit percentage and accusing others of greed. Ok buddy".gizmodo
Blockstream has issued an emergency Elements v23.3.4 patch and said functionary nodes are being updated. Its recovery plan calls for resuming block production with peg operations frozen, replaying verified transactions, and then restarting pegs once the network state is restored. The company warned that scammers are already impersonating Liquid and urged users to treat unsolicited outreach, "claim L-BTC" sites, and recovery-phrase requests as fraudulent.gizmodo